Assessment discipline
Criteria, review period, populations, sample selection and documented limits.
ATLANT SECURITY / SAMPLE AUDIT REPORT
Inspect the assessment.
Follow the conclusion.
A 30-page Microsoft 365 security audit for fictional Meridian Advisory Group AG. See how procedures, sampled records and operating evidence become findings your management team can act on.
30 pages · Searchable PDF · By Atlant Security
Fictional organisation and assessment; not client work.
A REPORT YOU CAN INTERROGATE
Read the population and sample selection. Inspect the procedures and sanitised records. Follow each finding from the observed condition to the recommended action and the evidence needed for closure.
Every organisation, record and result in this report is invented for illustration. It demonstrates reporting technique, not a completed client engagement, certification or statutory audit opinion.
INSIDE THE ASSESSMENT
Scroll through selected pages, then request
the complete report below.
An original, explicitly fictional Microsoft 365 audit. All organisations, procedures and records are illustrative.
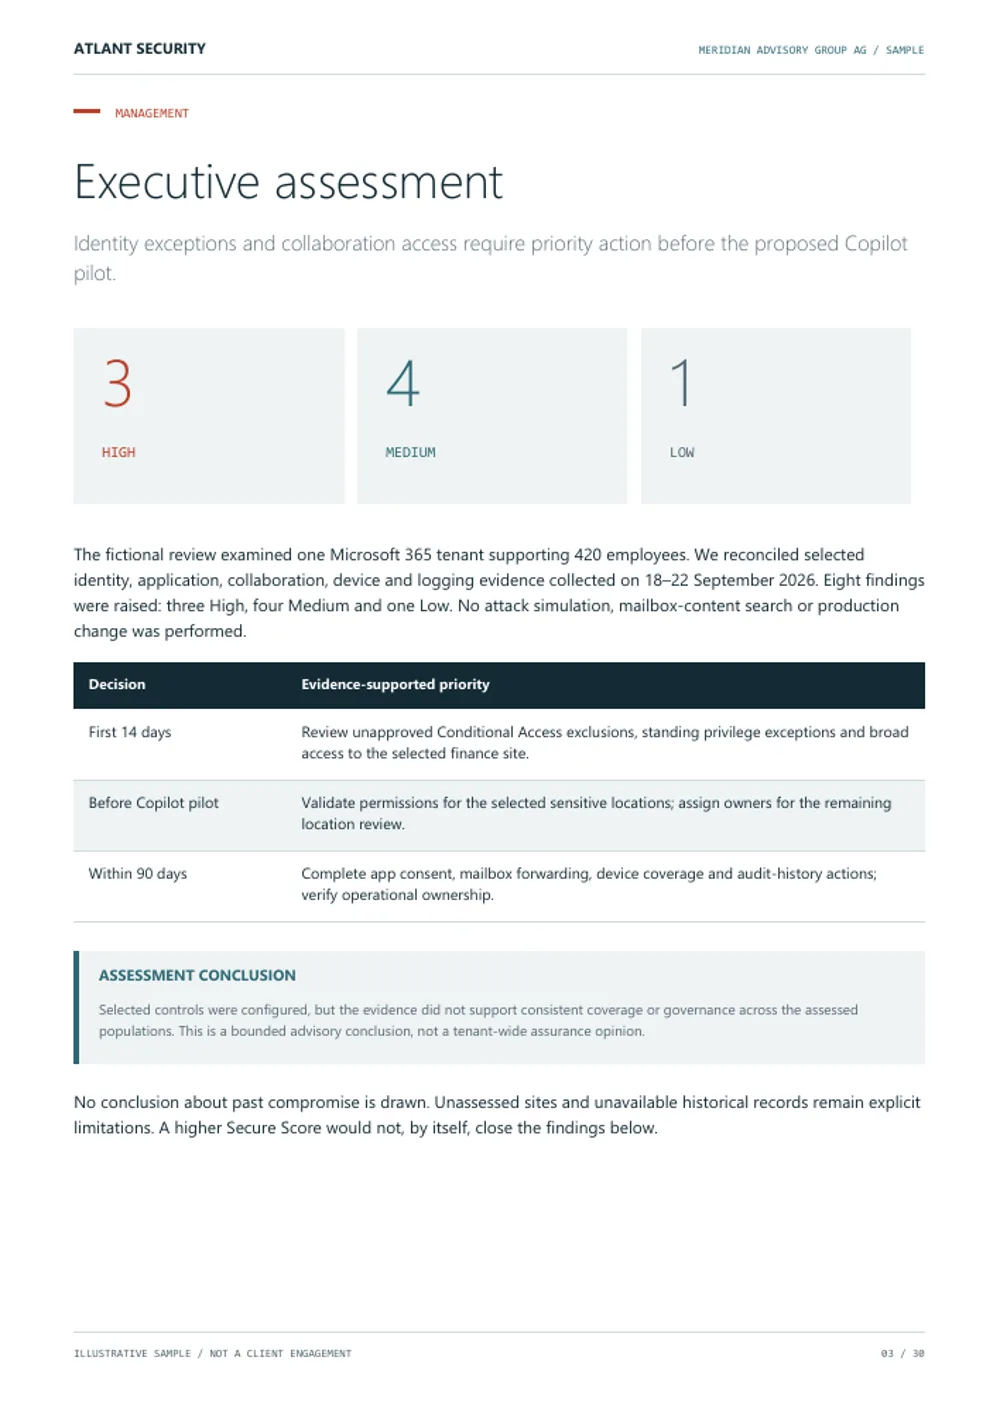
Eight findings: three High, four Medium and one Low. Management priorities connect identity exceptions, sensitive collaboration and operating evidence.
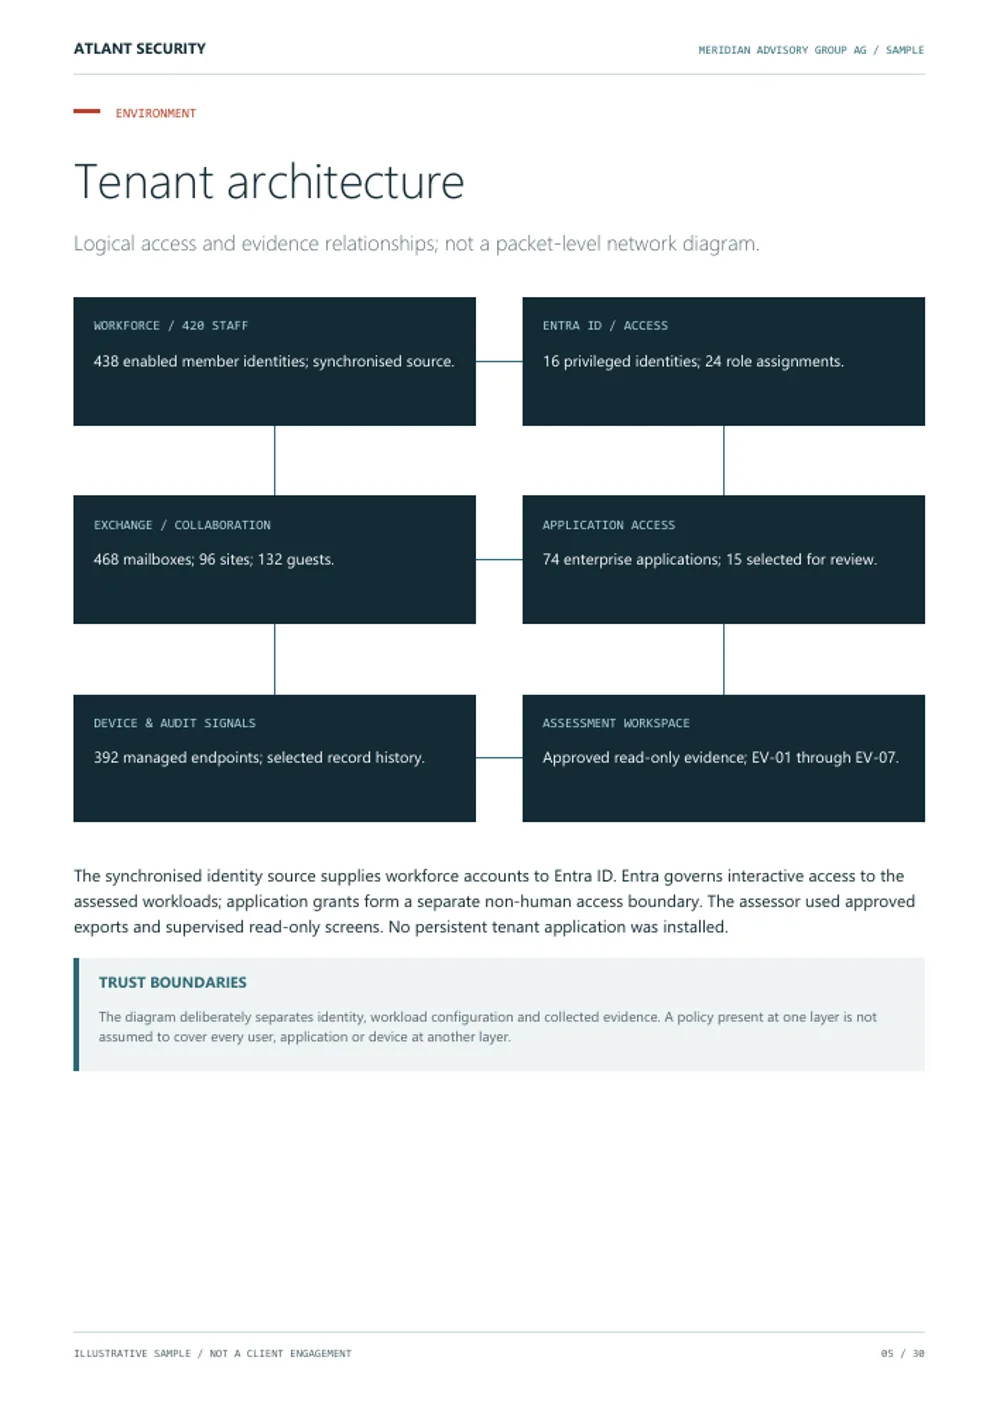
Logical relationships between workforce identities, Entra access, mail and collaboration, applications, devices and the assessment workspace.
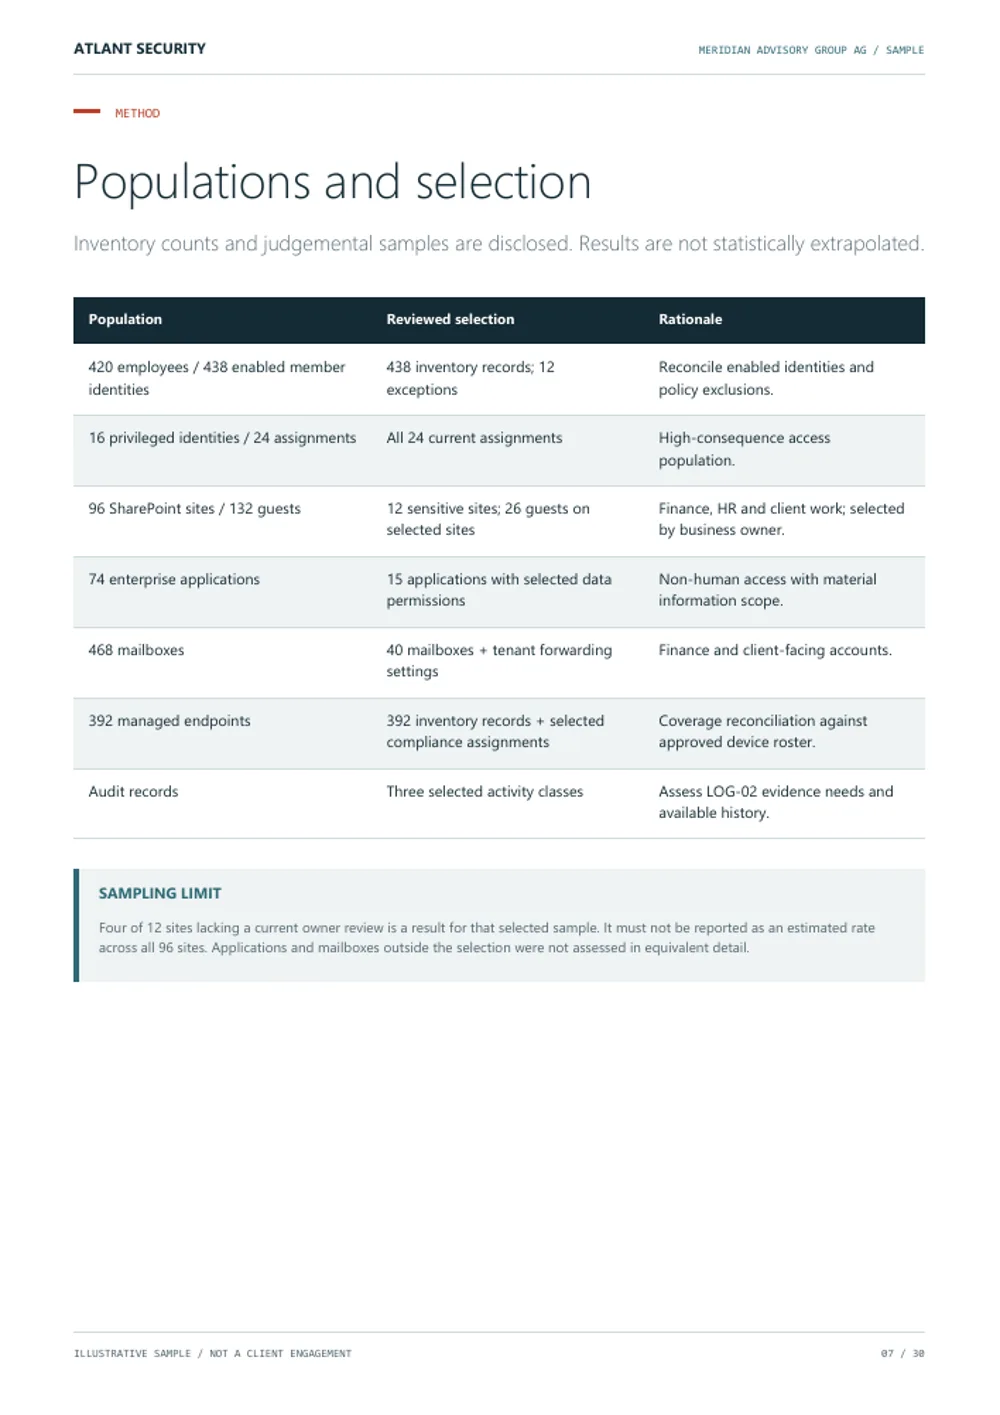
438 enabled member identities, 24 role assignments, 12 selected sites, 15 selected applications and defined mailbox and device populations. Samples are not statistically extrapolated.
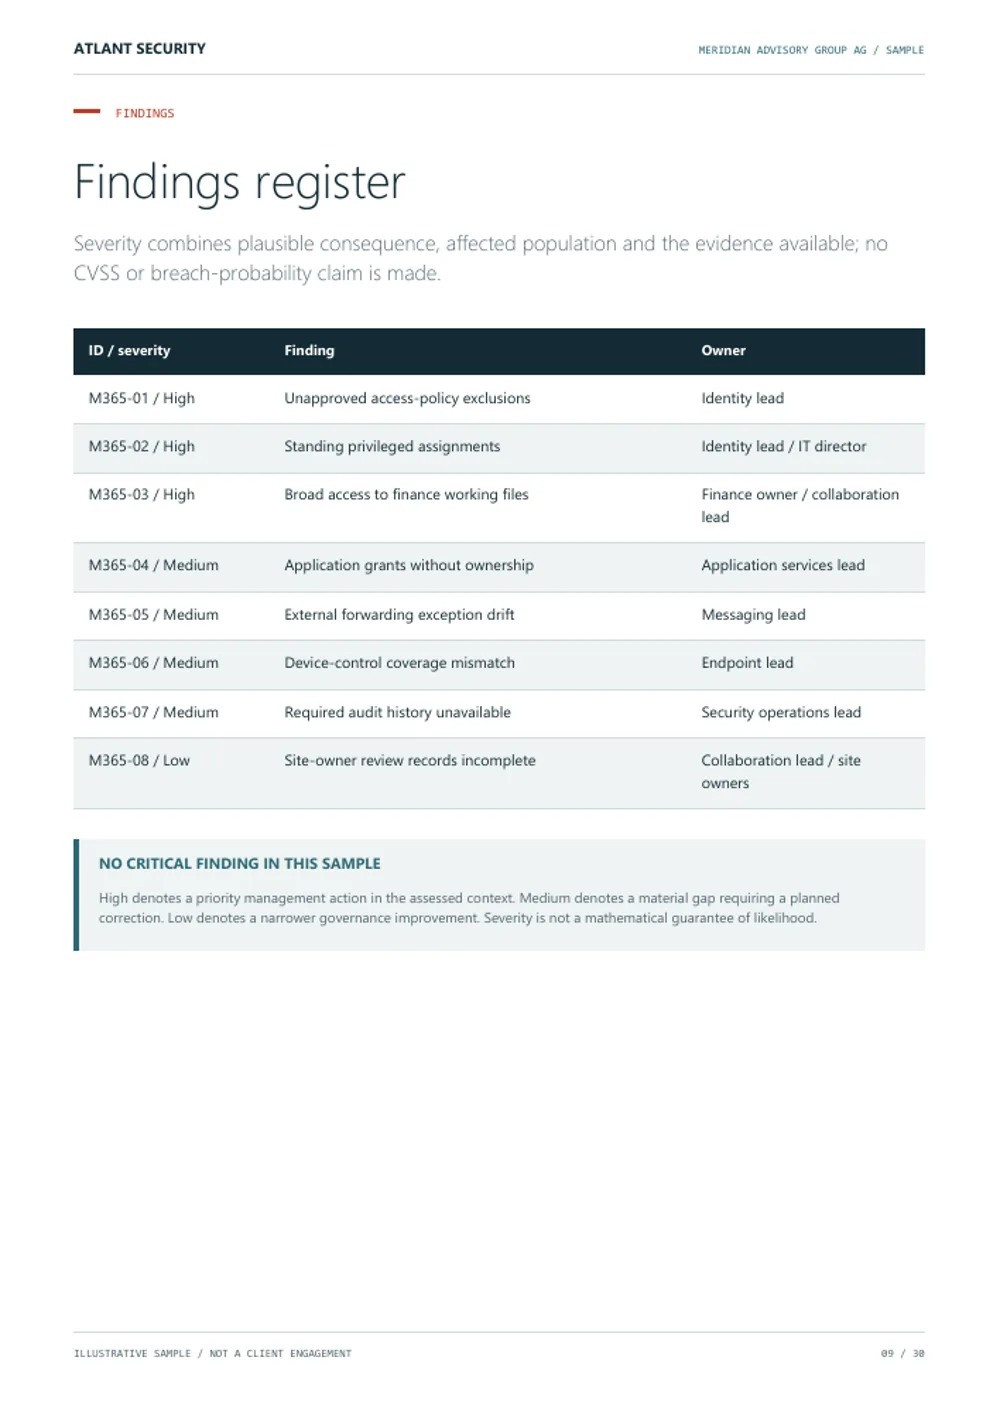
Eight findings connect evidence-supported conditions with severity and accountable owners.
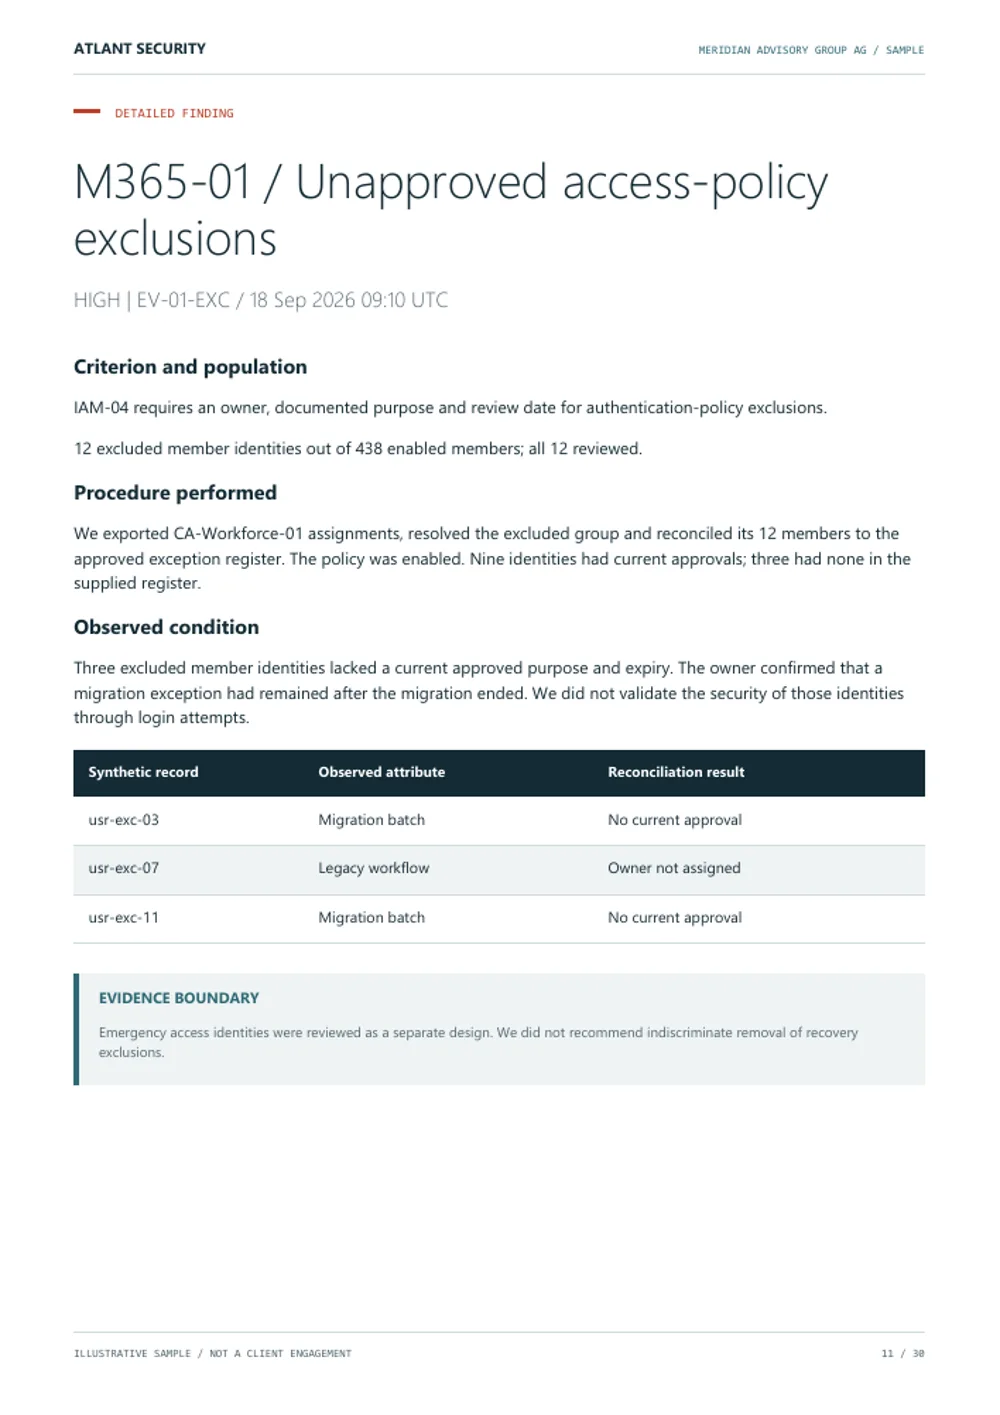
M365-01 reconciles 12 exclusions to the approved register. Three lacked current approval. The procedure, condition and evidence boundary are explicit.
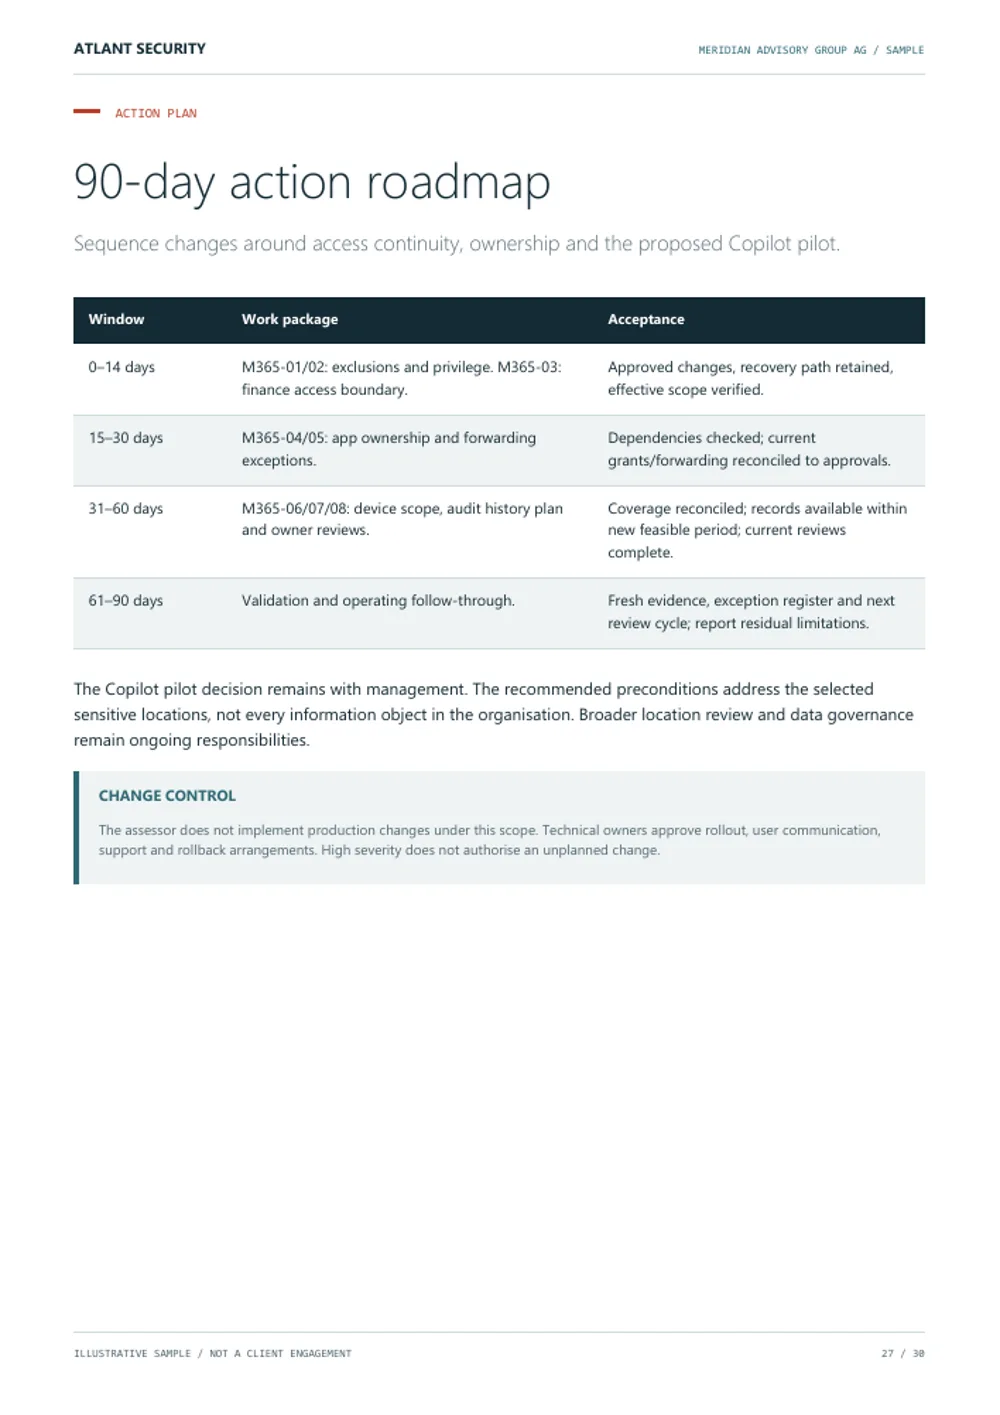
Sequence identity and collaboration corrections, app and messaging ownership, device and audit history work, then closure validation.
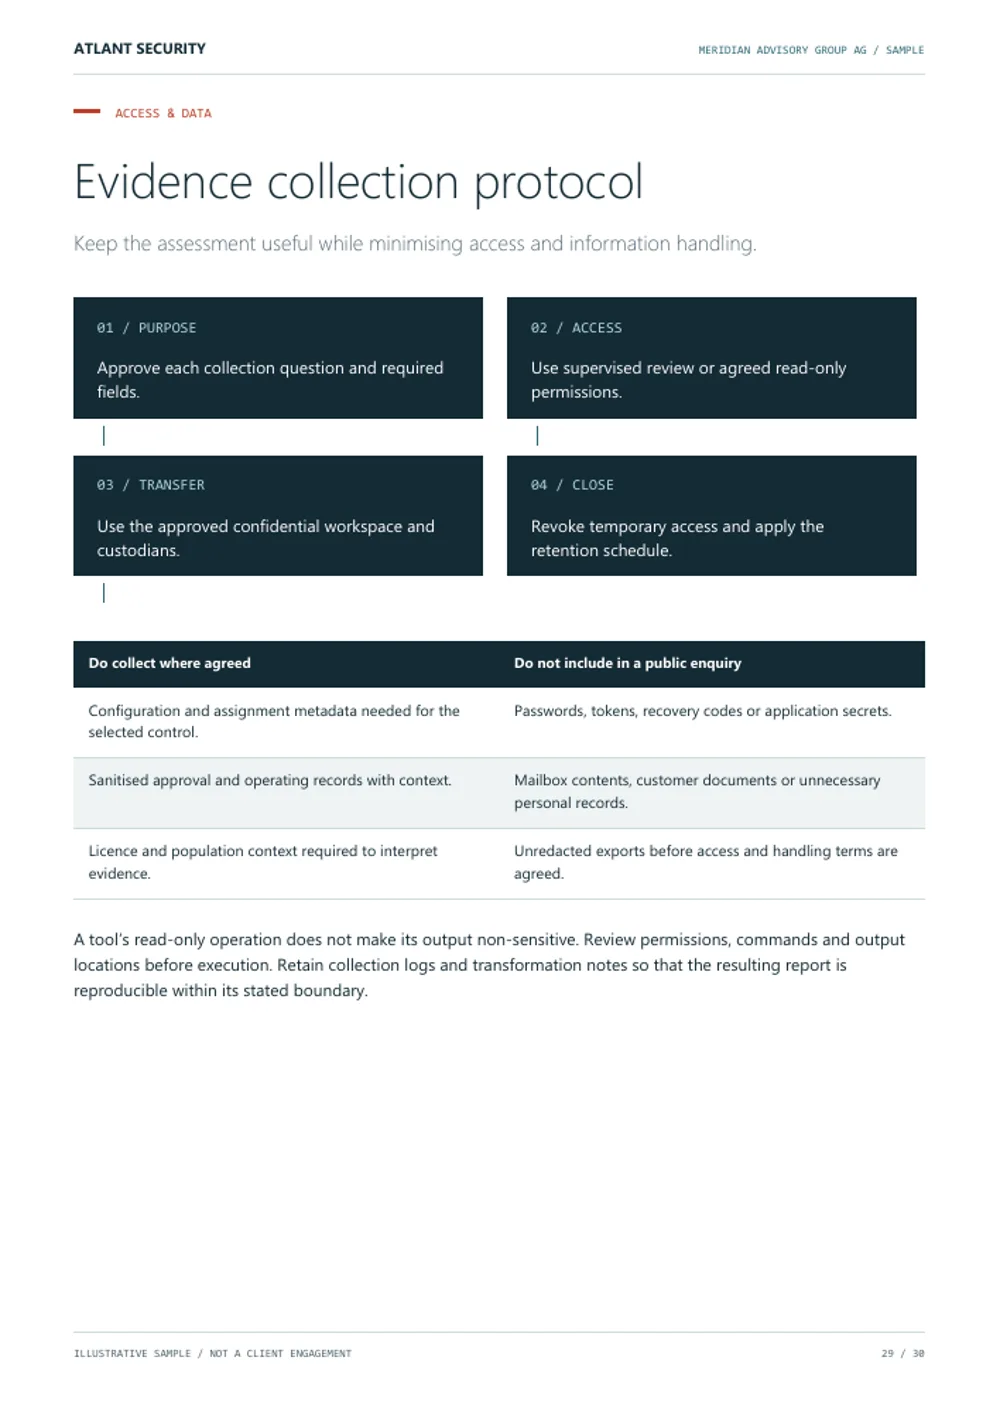
Purpose-limited collection, supervised or read-only access, approved transfer and revocation. No credentials or document contents in a public enquiry.
END OF THE PREVIEW
Get all eight findings, the evidence register, management response, limitations and closure protocol.
Get the complete sampleSelected page images and summaries are public. The full PDF is available after the form below.
BUILT FOR CRITICAL REVIEW
Criteria, review period, populations, sample selection and documented limits.
Policy exclusions, privileged assignments, collaboration permissions, app grants and device coverage.
Risk rationale, recommendations, accountable owners and explicit closure conditions.
A 90-day roadmap, responsibility model and example management response.
YOUR COPY OF THE SAMPLE
Use the example to discuss the evidence, reporting and follow-up you need.
Free PDF. Available immediately after submitting.
No newsletter subscription.
Tell us where to direct any follow-up about your request.
Your download access lasts for 15 minutes in this browser.
Download the 30-page PDFFictional organisation and assessment. Original sample by Atlant Security.
Need an alternative format? Contact our team.
No. Meridian Advisory Group AG and every record, finding and response are fictional. The report demonstrates assessment and reporting methods.
No. It demonstrates control and evidence assessment. Active technical testing requires its own authorised scope and procedures.
A scoped control assessment does not itself provide certification, statutory assurance or a universal compliance opinion. Confirm the precise requirement before commissioning work.
Yes. Upload your NDA or RFP in the contact form or the final brief step. Documents go to the team for human review and are not sent to AI.